Secrets walk out in prompts
API keys, .env values, database passwords and private keys flow into chat windows and agent pipelines. Once they leave, no recall exists — they sit in third-party logs forever.
Soteria is a local-first AI firewall. It inspects what your AI tools and agents send out, stops credential-bearing requests before they leave the machine, seals what matters in a post-quantum vault, and gives you revocable authority over every agent — then attacks its own defenses so you don’t have to.
simulated session · this monitor ships with the product
Every day, millions of developers and knowledge workers paste keys, credentials, private code, and unreleased ideas into AI tools. Those bytes go to third-party servers — irreversibly. Security software was never built for this.
API keys, .env values, database passwords and private keys flow into chat windows and agent pipelines. Once they leave, no recall exists — they sit in third-party logs forever.
AI agents get your credentials and broad permissions — with nothing structurally limiting where data travels or what they’re allowed to do. Excessive agency is now a top-10 AI security risk.
Credentials sit unencrypted across config files and history logs — no inventory, no monitor, no alert. And for individuals, the tools that do watch egress are corporate-only: priced, deployed, and closed.
Enterprises get DLP gateways. Individuals get nothing. Soteria closes that gap — on your own machine, under your own key.
Point your AI tools and agents at Soteria’s local guard. From that moment, every request is inspected inside encrypted tunnels — and the decision is made on your hardware, not in someone’s cloud.
Paste anything below — a prompt, a config snippet, a key. The same class of credential-shape detection the guard runs on live traffic evaluates it entirely in your browser. Like the product: nothing leaves your machine.
Use sample text, not real credentials. Ctrl or Command + Enter runs the check.
covers the shipping engine’s credential classes: OpenAI · Anthropic · Google · AWS · GitHub · Slack · Groq · HuggingFace · OpenRouter · PEM private keys · env-style secrets · prefixless high-entropy tokens. Shape-based by design — unknown formats pass, which is exactly why the product also ships canary credentials.
The screenshot below is the actual guard, running on an actual machine, captured while this page was being built — blocked attempts, inspected requests, and the append-only ledger of every verdict. Same engine. Same dashboard. Ships with the product.
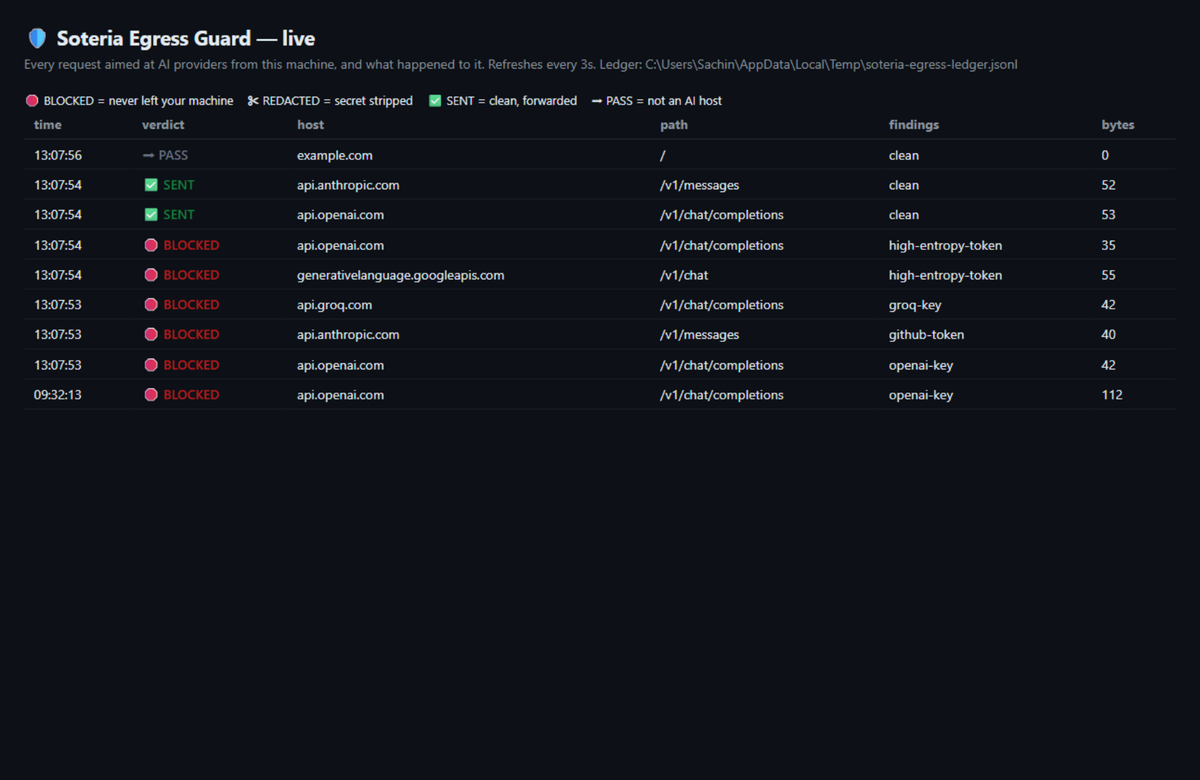
Six capabilities, one local core. Each is real, working, and battle-tested against live attacks — not a roadmap slide.
Inspect-and-stop gateway for AI provider traffic, with live monitoring and a permanent decision ledger. See every byte’s verdict in real time.
Seal secrets and whole files into opaque, size-padded blobs. The storage layer cannot read what it holds; every reveal asks you — per action.
Give agents scoped, expiring delegation tokens instead of raw credentials. Verify offline, deny scope creep automatically, revoke in seconds.
Pentest-grade scans of your own codebases: committed secrets, injection-prone AI prompts, unbounded agent actions. CI-gateable — a PR that breaks the shield fails the build.
The system attacks its own firewall with an adversarial corpus and reports containment. If any probe ever escapes, it exits non-zero — defenses that verify themselves.
Every security decision is appended, hash-chained, and inspectable — provable absence included. Trust built on evidence, not promises.
One binary, one machine, zero cloud. The firewall starts and its local certificate authority is trusted once — nothing about your setup changes.
Set a proxy variable for your terminals and agents, or route your browser. Everything that speaks to an AI provider now passes the guard.
The live dashboard shows every verdict as it happens; the ledger remembers them forever. Plant canary credentials and the system proves its own shield holds.
Soteria’s core uses hybrid post-quantum primitives — harvest-now, decrypt-later attacks have no future against what it seals today.
No account, no cloud, no telemetry. Keys are generated and used on your hardware and never leave it.
When verification can’t complete, the answer is no. An unreadable request is a blocked request — never a passed one.
Bucket-padded, opaque blobs mean the system’s own storage operator learns nothing — verified by adversarial tests on disk artifacts.
Every security decision lives in one audited core; every interface around it only presents and executes. No trust leaks through the UI layer.
Not marketing numbers — results from this build, produced by attacking it.
The self-pentest that found those four holes — and the fixes — is documented as a structured report for independent auditors. A full external audit is scheduled before any public release. That’s the bar.
System-wide protection with zero proxy configuration — the moment an AI tool speaks, the guard is already listening.
Mint and revoke agent delegations from your phone; your desktop agents obey — offline-verifiable.
Multi-device sync through anonymous tokens and an Oblivious HTTP relay network — the Blind Store, unbound from one machine.
“I kept watching brilliant people hand their hardest-won secrets to machines that don’t keep them. Soteria is my answer: a shield that runs where I run, answers only to me, and is strong enough to attack itself before anyone else can.”
Independent security-focused builder. I design and ship the whole stack myself — the cryptographic core, the firewall engine, the desktop and mobile clients — and I attack my own work before anyone else can. Soteria is built the way security software should be built: local-first, honest about its limits, and proven by evidence, not promises.
Software used to ask permission. Now it sends, stores, and shares by default — and calls it convenience.
I believe the next decade of AI belongs to the people who can prove their machines keep secrets — not trust that they do.
Soteria is built on a single conviction: your security should be a property you own — never a service you rent.
Soteria is in active development, hardened and running today on real machines. Leave your details and we'll contact you about early access.
No account or password required. By submitting, you agree to our Privacy Policy.
Questions? soteriaaisecurity@trustyourorigin.in